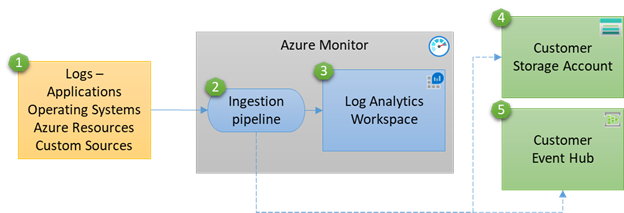
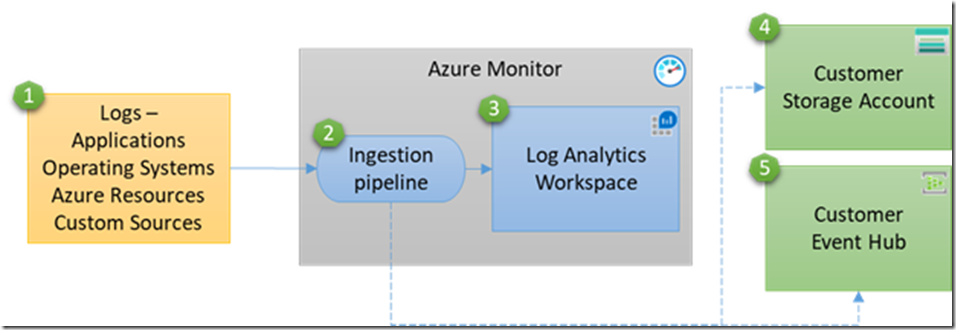
As it’s being collected, data from selected tables in your Log Analytics workspace can be continuously exported to an Azure storage account hourly or to Azure Event Hubs in near-real-time.
There isn't a way to filter data and limit the export to certain events. e.g. when configuring a data export rule for a SecurityEvent table. All the data sent to the SecurityEvent table is exported starting at the configuration time.
When exporting to Storage, each table is kept under a separate container. Similarly, when exporting to Event Hub, each table is exported to a new Event Hub instance, e.g. am-securityevent.
This data export preview provides several key advantages:
-
- Low cost data retention in storage
- Simpler compliance with auditing and security when longer data retention is involved
- Integration with Azure and third-party solutions such Azure Data Lake and Splunk
- Low latency export to Event Hub, allowing near-real-time monitoring and alerting
Learn more